DocuSend’s SOC 2 Type I Compliance
We are proud of the work we have done to manage risk and strengthen our information security program. Successfully completing the SOC 2 Type I examination demonstrates DocuSend’s continued commitment to maintaining controls and safeguards designed to protect our clients’ data.
Get Started
SOC 2 Type I
DocuSend completed a SOC 2 Type I examination performed by the independent CPA firm KirkpatrickPrice (https://kirkpatrickprice.com). The examination evaluates controls relevant to Security, Availability, Processing Integrity, and Confidentiality and provides an independent assessment of the controls designed and implemented by DocuSend as of the examination date.
DocuSend Enterprise Strengths Identified in SOC 2 Examination
1. DocuSend maintains a thorough hiring process designed to evaluate candidates for organizational, operational, and security fit. Candidates may meet with leadership at multiple levels of the organization as part of the hiring process.
2. DocuSend maintains policies and processes designed to support its obligations related to the handling of protected health information (PHI). The organization uses information security leadership and documented processes to identify, manage, and respond to potential security and privacy incidents. DocuSend also evaluates its information security policies against applicable security and compliance requirements and maintains documentation supporting these processes.
A Qualified Partner Makes All the Difference
We value partnerships that encourage education, quality, and value-based outcomes. We want to create positive change for our clients, and we want that from our own third-party relationships. Our audit partner is no different.
KirkpatrickPrice is an information security auditing firm whose goal is to make sure its clients are secure and compliant with whatever industry standards or customer demands they are facing. They seek to partner with clients and empower them to reach challenging compliance goals.
KirkpatrickPrice’s auditors make all the difference. They have been CTOs, CISOs, CSOs, and more. They understand the pressures clients are under as well as how difficult it is to become and stay compliant. That’s why they want to make sure every audit is worth it.
KirkpatrickPrice has completed over 20,000 audits and security assessments for over 2,000 clients worldwide.
Additionally, KirkpatrickPrice holds certifications with the following organizations:
Security & Compliance
With DocuSend, customers can leverage our security practices and independent examination as supporting information for their own security reviews, vendor-risk assessments, and compliance activities.
Compliance
You want to work with a firm that understands and supports your security and compliance efforts. With DocuSend, you can be sure you’ve chosen a partnership that will help you meet those goals. This means that parts of your own compliance have already been completed.
Data Security & Privacy
DocuSend maintains safeguards designed to protect customer data and support data security and privacy. Our information security program incorporates policies, controls, and operational processes designed to protect the confidentiality, integrity, and availability of information within the scope of our services.
Quality Audits
By working with KirkpatrickPrice on our SOC 2 Type I examination, DocuSend receives an independent assessment of the controls within the scope of the examination. The examination provides additional assurance and information for customers evaluating DocuSend’s security and control environment.
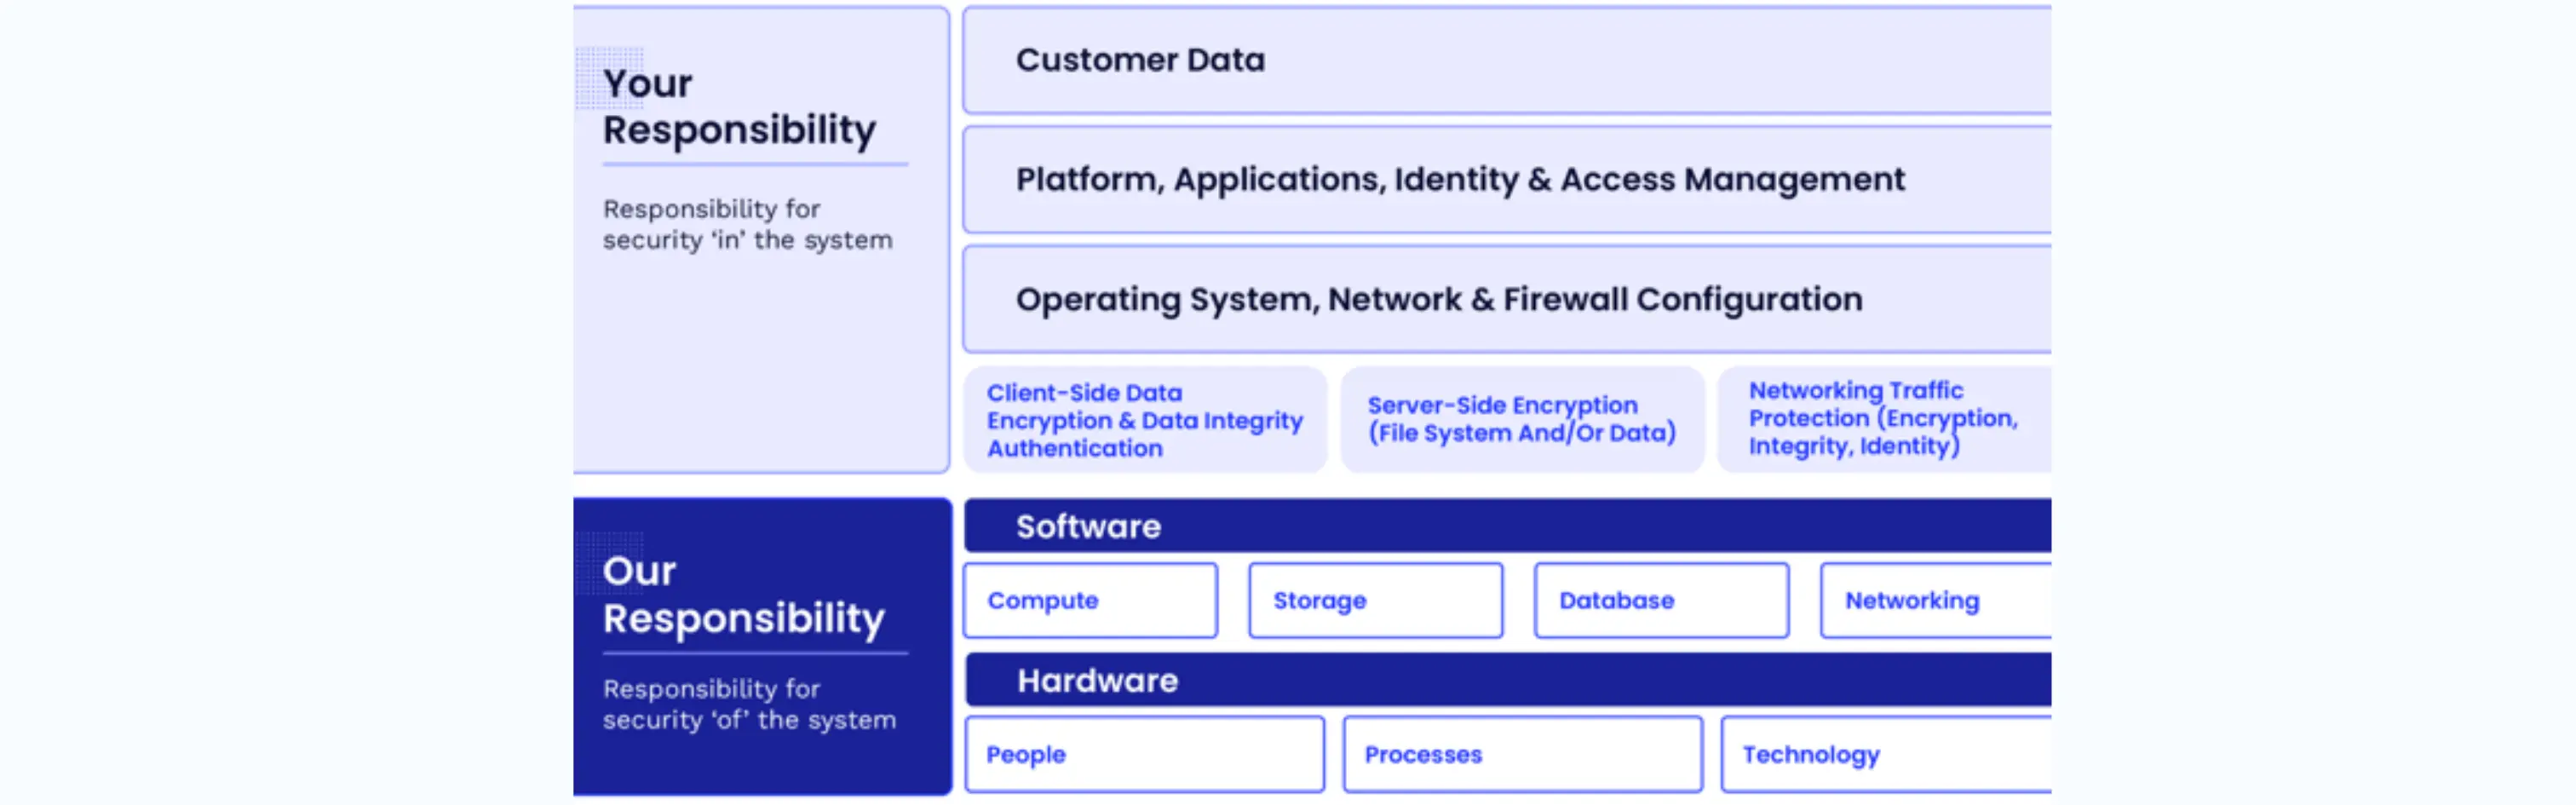
Security and Compliance are Shared Responsibilities
- DocuSend maintains controls designed to protect the systems and information supporting our services. Security is a shared responsibility between DocuSend and our customers.
- As a DocuSend client, you benefit from the security policies, controls, and operational processes that support the DocuSend service and have been included within the scope of our SOC 2 examination.
- As a DocuSend client, you are also responsible for the use and management of the system, and the data added to it.
- When these two elements work together properly, you can be confident in the security measures designed to protect your valuable data.
Compliance Results in Confidence
Completing our SOC 2 Type I examination represents an important milestone in DocuSend’s ongoing security and compliance program. We remain committed to maintaining and continually improving the controls and processes that support the security, availability, processing integrity, and confidentiality of our services.
SOC 2
This attestation provides evidence that DocuSend has a strong commitment to security and to delivering high-quality services to our clients by demonstrating that they have the necessary internal controls and processes in place.
What Our SOC 2 Type I Attestation Means for You
The SOC 2 Type I examination provides an independent assessment of relevant controls designed and implemented by DocuSend as of the examination date. The examination gives customers and prospective customers additional information to support their security reviews and vendor-risk assessments.
Security
DocuSend maintains controls designed to protect systems and customer information.
Availability
DocuSend maintains controls designed to support the availability and resilience of systems used to provide its services.
Processing Integrity
DocuSend maintains controls designed to support the complete, accurate, authorized, and timely processing of information.
Confidentiality
DocuSend maintains controls designed to protect confidential information in accordance with applicable commitments.
Built for Businesses That Handle Sensitive Documents
Businesses rely on DocuSend to automate the printing, preparation, and mailing of business-critical documents. Our SOC 2 Type I examination reinforces DocuSend's commitment to maintaining appropriate controls around the systems and information supporting these services.
Common document types include:
- ✓ Invoices
- ✓ Statements
- ✓ Notices
- ✓ Contracts
- ✓ Healthcare Documents
- ✓ Business Correspondence